|
Analysis North Korean hackers likely used new vulnerability to breach ROK defense firmResearchers link attacks against South Korean aerospace and nuclear research sectors to DPRK, warn of further breaches
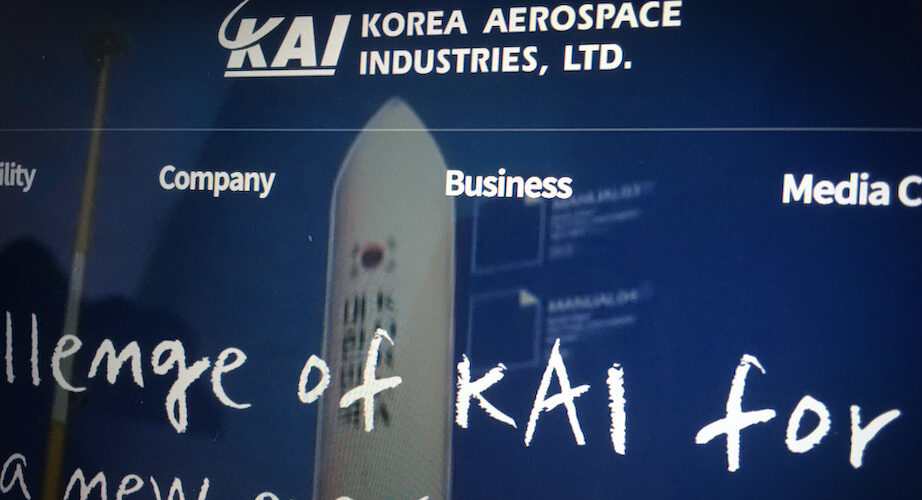 After a series of hacks against South Korea’s nuclear research and defense sectors, the cybersecurity firm TeamT5 said a group linked to North Korea likely used a previously unknown vulnerability and new malicious tools to break into the highly sensitive systems. According to a reportpublished on Wednesday, researchers said they believe a group labelled “CloudDragon” used a so-called zero-day exploit called MemzipRAT to install a backdoor and gain access to the organizations’ networks. The experts consider CloudDragon to be one of two sub-groups commonly referred to as Kimsuky, which has long been suspected of working on behalf of the © Korea Risk Group. All rights reserved. |


 SHARE
 COPY LINK
 X
 MASTODON

Recent Stories